Current Speakers

Kameliya Stoeva

Identity and Access Management Programme Manager

Kameliya Stoeva

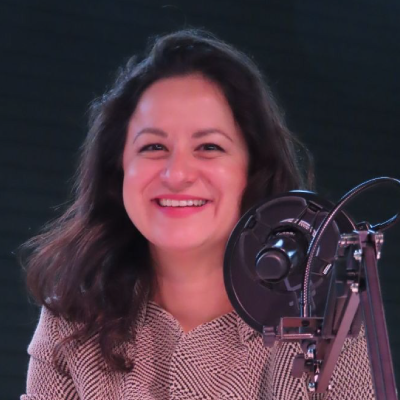
Cybersecurity and Identity & Access Management leader with over 8 years of experience working on identity and access management transformation and programmes in complex, regulated environments. As an IAM Programme Manager for KBC, Kameliya leads the strategic roadmap for identity services, focusing on Identity Governance, Zero Trust, Access Management, and readiness for emerging technologies such as Agentic AI.

Following nearly eight years in cybersecurity consulting at EY, she brings a combination of strategic vision, programme leadership, and deep IAM expertise. Kameliya is passionate about helping build trusted IAM ecosystems where security, compliance, and business agility reinforce one another.

Kameliya serves as the pioneering Chair of Belgium’s first IAM focused working group within the Belgian Cyber Security Coalition, helping drive collaboration and thought leadership around identity security, digital trust, and the future of IAM. She actively contributes to the cybersecurity and identity community as a conference speaker and mentor.

Pawel Bildziuk

Head of Identity and Access Management

Pawel Bildziuk

Andreas Avato

Global Channel Security Lead Corporate Bank

Andreas Avato

Susann Gäbler

Head of Risk Steering Fraud

Susann Gäbler

Susann Gäbler is a Risk Executive with more than 20 years of experience in banking, including 17 years in leadership roles. She is known for transforming risk and fraud functions into data-driven, scalable and business-enabling organizations. Her expertise spans fraud prevention, credit risk steering, governance and operating model transformation, with a particular focus over the last three years on building effective and scalable fraud prevention capabilities across portfolios and payment channels. As a speaker, she brings a pragmatic and forward-looking perspective on fraud prevention, risk transformation, leadership and data-driven steering in highly regulated environments.

Adrian Iacomi

Head of AI & Enablement

Adrian Iacomi

Nils Kaiser

Head of Bosch Engineering Austria

Nils Kaiser

Nils Kaiser is a seasoned professional with more than 15 years of experience in both automotive and non-automotive sectors, currently serving as the Managing Director for Business Consulting and Department Head of Bosch Engineering Austria within Robert Bosch AG.
Throughout his career, he has held prominent roles as a Senior Project Manager and Product Manager, honing his expertise in critical domains such as Cybersecurity, Automotive Automation, and the automation of Construction and Agricultural Machinery. He has successfully managed numerous internal R&D, grant-funded, and customer projects, showcasing his ability to navigate complex technical challenges and deliver impactful results.
Nils’s profound understanding of cutting-edge technologies and his strategic leadership skills make him a sought-after expert in the evolving landscape of intelligent systems and advanced engineering solutions. He is passionate about driving innovation and fostering collaborative environments to bring groundbreaking projects to fruition.

Philipp Wittek

Head of Sales EMEA

Philipp Wittek

Philipp Wittek is Head of Sales EMEA at Kiteworks, specializing in cybersecurity, data protection and the secure exchange of sensitive information. He works with organizations across Europe to address the growing challenges of data sovereignty, regulatory compliance and cyber resilience.

With a focus on practical security strategies, Philipp explores how organizations can move beyond contractual assurances to achieve genuine control over their data—including encryption, access, data location and governance. He regularly speaks on data security, sovereignty and compliance, helping organizations understand how secure data architectures can support both resilience and regulatory requirements.

Anmol Singh

Global Head (Identity and Access Management)

Anmol Singh

Anmol Singh is a seasoned cybersecurity leader with over two decades of expertise in designing and deploying enterprise-scale Identity & Access Management (IAM) solutions. Currently serving as Director & Global Head of IAM at Olympus Corporation, Anmol oversees the global IAM strategy, ensuring secure, efficient, and compliant identity frameworks that align with digital transformation and zero-trust initiatives.
Prior to Olympus, Anmol was Principal Product Manager at Microsoft, shaping Microsoft’s IAM product strategies at scale. His extensive background includes roles in IAM architecture, engineering, consulting, and program management across diverse industries, from enterprise IT environments to cloud-native platforms.
A recognized thought leader, Anmol regularly speaks at international cybersecurity conferences such as the European Identity & Cloud Conference, RSAC and other cyber security events, sharing practical insights on identity governance, privileged access management, consumer IAM and authentication innovations.
At Olympus, Anmol leads cross-functional teams driving IAM governance, privileged access security, automated lifecycle management, and passwordless solutions. He is passionate about leveraging IAM not just as a security enabler, but as a catalyst for organizational agility and innovation.
Beyond his professional role, Anmol actively mentors emerging cybersecurity talent and contributes to industry research and advisory boards, advocating for the evolution and maturity of identity security practices worldwide.

Valeria Castellani

Head of Security

Valeria Castellani

Valeria Castellani is Head of Security at Prada Group, where she leads the corporate security strategy across global operations. With direct field experience in high-risk environments, including armed escort operations in conflict zones, she brings a unique combination of operational expertise and strategic leadership to crisis management, organisational resilience, and integrated risk response.

Andrea Szeiler

Chief Information Security Officer

Andrea Szeiler

Andrea Szeiler is the Group CISO of MVM Ltd and President of Women4Cyber Hungary. She actively contributes to the cybersecurity community as a mentor, speaker, and member of several professional associations. Her mission is to empower women in IT security and support organizations in building risk-based, cost-effective security frameworks. Andrea is known for leading high-performing teams and fostering strategic partnerships across business and compliance domains. She believes cybersecurity is essential for all companies, regardless of size, and works to ensure resilient, secure operations.

Uko Valtenberg

Group CISO

Uko Valtenberg

Diana Prusova

Global Principal Product and Solutions Security Officer

Diana Prusova

Diana Průšová is the Global Principal Security and Solutions Officer at Yunex Traffic, where she leads the company’s global product security strategy for intelligent transportation systems and critical infrastructure. She is responsible for defining security strategy, driving secure-by-design product development, strengthening cyber resilience, and embedding security throughout the product lifecycle. Prior to joining Yunex Traffic, Diana held senior security leadership positions at several global technology companies, including serving as a Lead Security Solution Architect at Allied Irish Banks and Senior Security Program Manager at Pure Storage. Throughout her career, she has led global security transformation initiatives spanning product security, infrastructure security, cloud security, AI security, and enterprise security strategy. She has also provided executive leadership during major cybersecurity incidents including log4j, guiding organizations through complex security challenges.

Diana is recognized for her leadership in AI security, having led AI security architecture, security testing, and red teaming initiatives for AI-enabled products. Her work focuses on building AI systems with well- understood and well-managed risks, integrating security throughout the AI lifecycle, and helping organizations adopt AI technologies in high-assurance and critical infrastructure environments.

Beyond her industry role, Diana serves as an advisor to ENISA, contributing to the implementation of the Cyber Resilience Act, strengthening Europe’s cyber resilience and reducing strategic technology dependencies. She is also a voting member of the global FIRST CVSS Special Interest Group, contributing to the evolution of CVSS v4.0 and advancing industry best practices in vulnerability management.

Diana is an author of cybersecurity research publications and industry papers, an active mentor to emerging cybersecurity professionals, and a contributor to international cybersecurity communities. Her work bridges executive leadership with hands-on technical expertise, helping organizations strengthen product security, secure-by-design AI, resilient products, and critical infrastructure capable of withstanding the next generation of autonomous cyber threats.

Francesco Aicardi

Advisor

Francesco Aicardi

Francesco works at the European Commission, where he focuses on digital identity and trust within DG CNECT. Prior to this, he held managerial roles at Nexi Group and McKinsey & Company. He also gained public sector experience at the Italian Government, serving in the Presidency of the Council of Ministers. Francesco holds a Bachelor’s degree in Business Administration from Bocconi University and a Master’s degree in Management from London Business School.

Dr. Ioana Teodoreanu

Head of Governance Planning

Dr. Ioana Teodoreanu

Holding a PhD in Industrial Engineering, Dr. Ioana Teodoreanu brings together academic rigour and hands-on industry experience. As Head of Governance Planning at AUMOVIO Germany GmbH, she bridges Product Cybersecurity, Safety, and AI, and drives corporate governance, turning regulatory, customer, and business requirements into actionable governance frameworks: from policies, manuals, and standards to operational practice, compliance ready (e.g. under the EU AI Act, Cyber Resilience Act, ISO/SAE 21434, ISO/IEC 42001, ISO 26262, ISO/PAS 21448 etc.). With a career built across cybersecurity governance, supplier quality, and organisational transformation in the automotive industry, she has led the development of management systems, enterprise risk controls, and supplier risk strategies across complex international organisations. Certified Automotive SPICE® Principal Assessor and active contributor to the intacs Cybersecurity Working Group, she is among the practitioners actively shaping how cybersecurity processes and standards are defined, interpreted, and applied across the automotive industry.

Sven Hezel

CEO and Founder

Sven Hezel

Can Yildiz

Independent Consultant

Can Yildiz

Eduard Singer

Managing Partner

Eduard Singer

Sina Yazdanmehr

Founder

Sina Yazdanmehr

Sina is founder and managing director of Aplite GmbH, a Berlin-based cybersecurity consultancy. With over a decade of experience in IT security, he has served as interim CISO for several companies across Europe. He works across both ends of the discipline, from hands-on cloud and application security to building secure and scalable identity and access management programs, and advising C-level stakeholders on security strategy.

Ray Irving

Former CISO

Ray Irving

Ray Irving brings 20 years of information security leadership in financial services, most recently serving three years as CISO at Sygnum Bank, a FINMA-regulated digital assets bank. Before that he spent eight years as Managing Director EMEA at FS-ISAC, the financial sector’s threat intelligence and resilience non-profit, where he collaborated with member CISOs and represented the sector to government agencies, central banks and ENISA.

Previously he was Head of Security Programs at UBS and held security related roles at Citibank and Lombard Odier. He holds CISSP, CRISC and PMP certifications.

Irina Rosensaft

Head of Programm Office NOOTS

Irina Rosensaft

Irina Rosensaft is an experienced leader in digital transformation, working at the intersection of IT, organizational processes, and civil society.

In her roles she develops strategies to strengthen digital resilience and effectively address current and emerging challenges in the digital world and cybersecurity. With a background in political science and extensive experience in process optimization, change management and cyber security, Irina bridges the gap between technology, governance, and organizational and societal requirements. She is passionate about advancing cybersecurity solutions, aiming to help shape a secure and innovative digital future.
Carine Hohmann

AI Governance, AI Security & GRC Consultant

Carine Hohmann

Carine Hohmann is a cybersecurity, AI governance and GRC professional with a strong focus on security, risk and emerging technology. She is an ISO/IEC 27001 Lead Implementer and Lead Auditor, an ISO/IEC 42001 Lead Auditor, and CISSP-certified.

Her work focuses on helping organisations translate security, risk and regulatory requirements into practical governance and control frameworks, with a particular interest in AI security, AI governance, identity and digital risk. She brings a cross-functional perspective that connects cybersecurity, governance, compliance and business needs.
Carine is passionate about making complex security and emerging technology topics accessible and actionable, and regularly engages in discussions around responsible AI, cybersecurity, risk management and regulatory developments.
She is based in Germany and works at the intersection of cybersecurity, GRC and the rapidly evolving AI landscape

Andres Maurer

Executive Chair

Andres Maurer

Andres has nearly 30 years of IT experience, including two decades in the financial sector. Over his career, he has held leadership roles as Project Manager, Head of Testing, and Product Owner, working across industries such as power generation, pharmaceuticals, aviation, healthcare, and financial services.


He led notable projects for Roche and Lufthansa Technik, while his Identity and Access Management initiative at Swiss Re received the KuppingerCole European Identity & Cloud Award in 2013 for Best Access Governance and Intelligence Project. Most recently, he worked at a major international Swiss bank, first leading business analysis in cyber security and later was responsible for secure digital banking connectivity. Motivated by protecting the public from cybercrime, he developed a framework to combat online scams. His current focus is on Cyber Fraud Resilience and Agentic AI.

John Erik Setsaas

Principal Advisor and Founder

John Erik Setsaas

Amela Gjishti

Vice President

Amela Gjishti

Amela Gjishti is an AI Cybersecurity Architect responsible for AI risks in enterprise environments and Vice President of Women in Cybersecurity AI Affiliate. She is a certified AI Governance Professional and has worked with the EU AI Act since 2021. She has acquired professional experience in the cybersecurity domain internationally within the financial industry, as well as AI Governance in Big 4 consulting. She aspires to build secure AI and Agentic systems through the lens of traditional cybersecurity and the strong emphasis of the non-deterministic nature of AI. 

Kinfos Events (UK) Pvt Ltd. (HQ):
506 Milton Road,
Broughton Milton Keynes,
England MK10 9RJ,
United Kingdom
Phone:+44 (0)207 0787651
Kinfos Events (India) Pvt Ltd.
No. 3, Ground Floor,
Unitech Cyberpark, Sector-39,
Gurgaon -122003,
Haryana, India

Newsletter

    Copyright © 2024 Kinfos Events Private Limited with number 07713454, registered office 506 Milton Road, Broughton, Milton Keynes, England, MK10 9RJ